From fa64a98019dde4e25492722bb8009dae7fefd863 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Tue, 6 Dec 2022 22:27:06 -0800
Subject: [PATCH 01/41] Update ReadmeFile - with initial small changes
---
README.md | 2 +-
1 file changed, 1 insertion(+), 1 deletion(-)
diff --git a/README.md b/README.md
index 16e1160e..706c6d5b 100644
--- a/README.md
+++ b/README.md
@@ -86,7 +86,7 @@ However, one of the many advantages of the open source software model is that th
The quickest and easiest way to install the software is to download the most recent "seedsigner_X_X_X.zip" file in the [software releases](https://github.com/SeedSigner/seedsigner/releases) section of this repository.
-After downloading the .zip file, extract the seedsigner .img file, and write it to a MicroSD card (at least 4GB in size or larger). Then install the MicroSD in the assembled hardware and off you go.
+After downloading the .zip file, verify it, extract the seedsigner .img file, and write it to a MicroSD card (at least 4GB in size or larger). Then install the MicroSD in the assembled hardware and off you go.
## Verifying the Software
You can verify the data integrity and authenticity of the latest release with as little as three commands. This process assumes that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal) and have navigated to the folder where you have these four relevant files present: (This will most likely be your Downloads folder.)
From 86a5d1fa605239f072c3fd29d20e205476e5406a Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Tue, 6 Dec 2022 22:45:23 -0800
Subject: [PATCH 02/41] A Heading change
---
README.md | 2 +-
1 file changed, 1 insertion(+), 1 deletion(-)
diff --git a/README.md b/README.md
index 706c6d5b..9b8df237 100644
--- a/README.md
+++ b/README.md
@@ -77,7 +77,7 @@ Notes:
# Software Installation
-## Special Note on Minimizing Trust
+## A Special Note on Minimizing Trust
As is the nature of pre-packaged software downloads, downloading and using the prepared SeedSigner release images means implicitly placing trust in the individual preparing those images; in our project the release images are prepared and signed by the eponymous creator of the project, SeedSigner "the person". That individual is additionally the only person in possession of the PGP keys that are used to sign the release images.
However, one of the many advantages of the open source software model is that the need for this kind of trust can be negated by our users' ability to (1) review the project's source code and (2) assemble the operating image necessary to use the software themselves. From our project's inception, instructions to build a SeedSigner operating image (using precisely the same process that is used to create the prepared release images) have been made availabile. We have put a lot of thought and work into making these instructions easy to understand and follow, even for less technical users. These instructions can be found [here](docs/manual_installation.md).
From 5a1bb41601f55d7d167ebbe4710090ed2a51e9f7 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Tue, 6 Dec 2022 22:54:40 -0800
Subject: [PATCH 03/41] minor spelling fixes
---
README.md | 4 ++--
1 file changed, 2 insertions(+), 2 deletions(-)
diff --git a/README.md b/README.md
index 9b8df237..37a5067e 100644
--- a/README.md
+++ b/README.md
@@ -46,7 +46,7 @@ If you have specific questions about the project, our [Telegram Group](https://t
### Considerations:
* Built for compatibility with Specter Desktop, Sparrow, and BlueWallet Vaults
* Device takes up to 60 seconds to boot before menu appears (be patient!)
-* Always test your setup before transfering larger amounts of bitcoin (try testnet first!)
+* Always test your setup before transferring larger amounts of bitcoin (try Testnet first!)
* Taproot not quite yet supported
* Slightly rotating the screen clockwise or counter-clockwise should resolve lighting/glare issues
* If you think SeedSigner adds value to the Bitcoin ecosystem, please help us spread the word! (tweets, pics, videos, etc.)
@@ -77,7 +77,7 @@ Notes:
# Software Installation
-## A Special Note on Minimizing Trust
+## A Special Note On Minimizing Trust
As is the nature of pre-packaged software downloads, downloading and using the prepared SeedSigner release images means implicitly placing trust in the individual preparing those images; in our project the release images are prepared and signed by the eponymous creator of the project, SeedSigner "the person". That individual is additionally the only person in possession of the PGP keys that are used to sign the release images.
However, one of the many advantages of the open source software model is that the need for this kind of trust can be negated by our users' ability to (1) review the project's source code and (2) assemble the operating image necessary to use the software themselves. From our project's inception, instructions to build a SeedSigner operating image (using precisely the same process that is used to create the prepared release images) have been made availabile. We have put a lot of thought and work into making these instructions easy to understand and follow, even for less technical users. These instructions can be found [here](docs/manual_installation.md).
From 4f910cf3ef894e89e39376b84526594083909eb6 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Wed, 7 Dec 2022 01:03:26 -0800
Subject: [PATCH 04/41] Rewrite the software Download, & Verify sections
---
README.md | 94 +++++++++++++++++++++++++++++++++++++++----------------
1 file changed, 67 insertions(+), 27 deletions(-)
diff --git a/README.md b/README.md
index 37a5067e..f0c20789 100644
--- a/README.md
+++ b/README.md
@@ -84,54 +84,94 @@ However, one of the many advantages of the open source software model is that th
## Downloading the Software
-The quickest and easiest way to install the software is to download the most recent "seedsigner_X_X_X.zip" file in the [software releases](https://github.com/SeedSigner/seedsigner/releases) section of this repository.
+To download the most recent software version, click here [here](https://github.com/SeedSigner/seedsigner/releases), and then expand the *Assets* sub-heading.
+Download these files to your computer.
+1. seedsigner_0_5_x.img.zip
+2. seedsigner_0_5_x.img.zip.sha256
+3. seedsigner_0_5_x.img.zip.sha256.sig
-After downloading the .zip file, verify it, extract the seedsigner .img file, and write it to a MicroSD card (at least 4GB in size or larger). Then install the MicroSD in the assembled hardware and off you go.
+After the files have finished downloading, follow the steps below to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the power. Wait about 45 secs for our logo to appear.
-## Verifying the Software
-You can verify the data integrity and authenticity of the latest release with as little as three commands. This process assumes that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal) and have navigated to the folder where you have these four relevant files present: (This will most likely be your Downloads folder.)
+**Note:** The version numbers of the latest files will be higher than this example, but the naming format will be the same.
-* seedsigner_pubkey.gpg (from the main folder of this repo)
-* seedsigner_0_4_6.img.zip (from the software release)
-* seedsigner_0_4_6.img.zip.sha256 (from the software release)
-* seedsigner_0_4_6.img.zip.sha256.sig (from the software release)
-**Note:** The specific version number of the files in your folder might not match the above exactly, but their overall format and amount should be the same.
+## Verifying that the downloaded files are authentic (optional but recommended!)
+You can quickly verify that the downloaded software is both genuine and unaltered, by following these instructions.
-This process also assumes you are running the commands from a system where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are installed and working.
+This step assumes you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal)
+Begin in the same folder where you have saved the download files.
+(Which will most likely be your Downloads folder.)
-First make sure that the public key is present in your keychain:
+
+###Import the public key of the SeedSigner Project into your computer
+The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
+The Keybase.io website service allows you to verify that the key belongs to the organization it claims to represent. It is checked cryptographically and saved in 3 separate online locations (Twitter, Seedsigner.com and github.com)
+
+If you need more information, open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
+
+else simply run this command (inside the same folder as the downloaded files):
```
-gpg --import seedsigner_pubkey.gpg
-```
-This command will import the public key, or return:
-```
-key <...> not changed
+gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
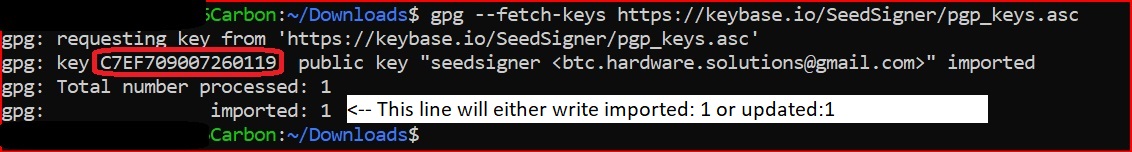
+When the command completes successfully, it will display a numeric ID, as circled in red in the example below. We will use that numeric ID in the next step.
+
+
+
+###Verifying that your signature file is signed by the right person(s)
+
+The next steps will allow you how to confirm that your downloaded .zip file is the genuine and unaltered SeedSigner software.
+
+The *verify* command below, identifies *who exactly* made the signature file.
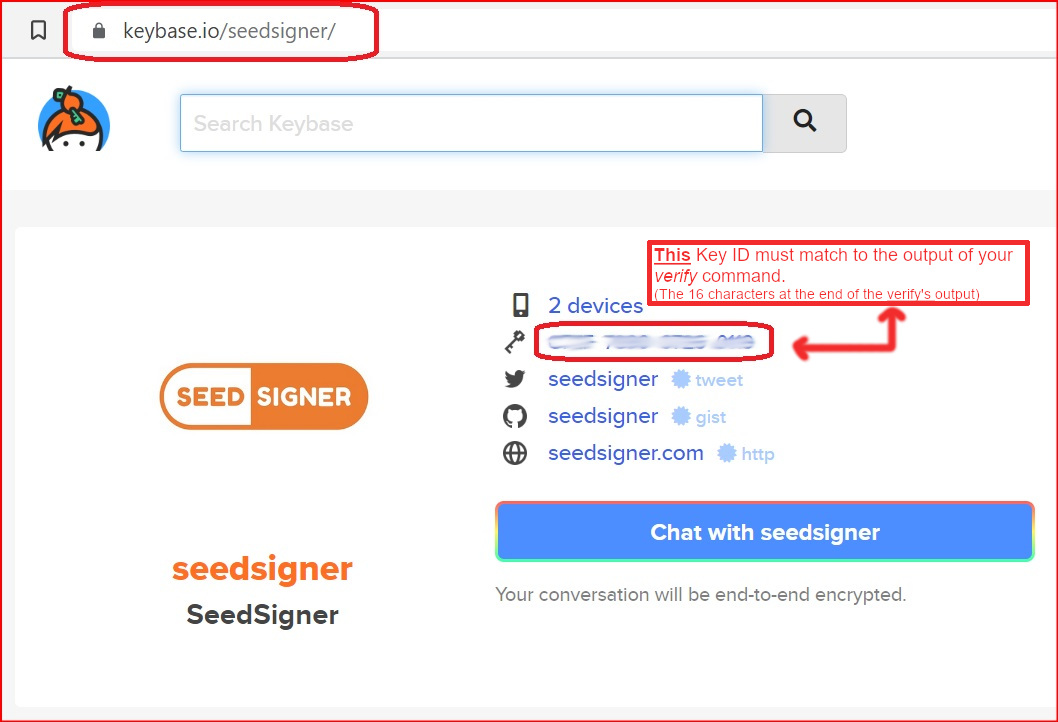
+The output of this verify command is the all-important *signers* fingerprint, and it is this fingerprint that you will visually (and match!) to the fingerprint ID shown at Keybase.io/SeedSigner. If the ID matches, then you know it was seedsigner who signed it.
+
+(More specifically, the verify command determines *which* key pair already on your computer, signed the sha256.sig file. It does this comparing the file cryptographically to its unsigned equivalent (the .sha256 file).)
-Now you can verify the authenticity of the small text file containing the release's SHA256 hash with the command:
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
```
-**Note:** The `*`s in the command above allow the terminal to auto-populate the command with the version number you have in the folder you are in. It should be copied and pasted as is.
+**Note:** The `*`s in the command will auto-match to the version number in your current folder. It should be copied and pasted as-is.
-The reponse to this command should include the text:
-```
-Good signature from "seedsigner
+ The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent.
+ Keybase has checked the pubkey cryptographically when it was saved in the 3 separate online locations. These are: on www.twitter.com/seedsigner, on the website www.seedsigner.com , and in the software repository at Github www.github.com/seedsigner.
+ You can verify those 3 separate Key locations yourself, by clicking the 3 blue badges on www.keybase.io/seedsigner. (The Twittter blue badge one is the most human-readble.)
+
+ If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
+
+
+More specifically, the verify command determines *which* key pair of those already installed on your computer, actually signed the sha256.sig file. It does this by cryptographically comparing the sha25.sig file to its unsigned equivalent (the .sha256 file), looping through the public keys already imported into your computer. whichever installed/imported key is able to perform the comparision successfully, then that is the pubkey of the keypair that was used!
+
+
+If the response displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
+
+If you receive the warning message below, it can be safely ignored *because* you are going to be matching the fingerprint ID manually, to Keybase.io/seedsigner.
+
+> gpg: WARNING: This key is not certified with a trusted signature!
+> gpg: There is no indication that the signature belongs to the owner.
+
+
+If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID. you must now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner. If the fingerprint ID matches, then you have successfully verified that seedsigner signed the software you have just downloaded.
+
+If it does not match perfectly, then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
+
+
+
+The final verification step is to make sure that the other downloaded files (eg the files inside the zip file) were not altered or added to in any way. Even a single character being changed or removed, would show up here.
+
+**On Linux or OSX**
```
shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
```
-The reponse to this command should include the text:
+
+**On Windows (Powershell)**
```
-seedsigner_0_4_6.img.zip: OK
+CertUtil -hashfile seedsigner_0_*_*.img.zip SHA256 | findstr /v "hash"
```
-There are other steps you can take to verify the software, including examining the hash value in the .sha256 text file, but this one has been documented here because it seems the simplest for most people to follow. Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and assumes the private key has remained uncompromised and is not being used by a malicious actor.
+The response must include the text **seedsigner_[VersionNumber].img.zip OK**, like this:
+```
+seedsigner_0_5_x.img.zip: OK
+```
+**If you have received the OK message above then your verification has suceeded! - well done, the download files are now all confirmed as authentic and unaltered**!
+If the result did not display "OK", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
+
+Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and their private key is not compromised or somehow being used by a malicious actor.
---------------
# Enclosure Designs
From 69dc06ca6fcfc174c5f067ac567c3ddc71cf48c8 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Wed, 7 Dec 2022 01:39:43 -0800
Subject: [PATCH 05/41] Minor edits to download and veryify sections.
---
README.md | 56 +++++++++++++++++++++++++++++++------------------------
1 file changed, 32 insertions(+), 24 deletions(-)
diff --git a/README.md b/README.md
index f0c20789..a7093816 100644
--- a/README.md
+++ b/README.md
@@ -84,32 +84,34 @@ However, one of the many advantages of the open source software model is that th
## Downloading the Software
-To download the most recent software version, click here [here](https://github.com/SeedSigner/seedsigner/releases), and then expand the *Assets* sub-heading.
-Download these files to your computer.
+To download the most recent software version, click [here](https://github.com/SeedSigner/seedsigner/releases), and then expand the *Assets* sub-heading.
+Download these files to your computer:
1. seedsigner_0_5_x.img.zip
2. seedsigner_0_5_x.img.zip.sha256
3. seedsigner_0_5_x.img.zip.sha256.sig
-After the files have finished downloading, follow the steps below to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the power. Wait about 45 secs for our logo to appear.
+Once the files have all finished downloading, follow the steps below to verify and to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can being using your Seedsinger!
**Note:** The version numbers of the latest files will be higher than this example, but the naming format will be the same.
## Verifying that the downloaded files are authentic (optional but recommended!)
-You can quickly verify that the downloaded software is both genuine and unaltered, by following these instructions.
+You can quickly verify that the downloaded software is both authentic and unaltered, by following these instructions.
+
+This step assumes you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
-This step assumes you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal)
Begin in the same folder where you have saved the download files.
(Which will most likely be your Downloads folder.)
-###Import the public key of the SeedSigner Project into your computer
+### Import the public key of the SeedSigner Project into your computer
+
The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
-The Keybase.io website service allows you to verify that the key belongs to the organization it claims to represent. It is checked cryptographically and saved in 3 separate online locations (Twitter, Seedsigner.com and github.com)
+The Keybase.io website service allows you to independently verify that the key is authentic and that it belongs to the organization it claims to represent. Keybase has checked it cryptographically and it has saved and matched in 3 separate online locations (On Twitter, on the Seedsigner.com website and lastly in the github.com/seedsigner software repository).
-If you need more information, open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
+If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
-else simply run this command (inside the same folder as the downloaded files):
+Now run this command (from inside the same folder that you saved the downloaded files into):
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
@@ -117,48 +119,49 @@ When the command completes successfully, it will display a numeric ID, as circl

-###Verifying that your signature file is signed by the right person(s)
+### Verifying that your signature file is signed by the right person(s)
-The next steps will allow you how to confirm that your downloaded .zip file is the genuine and unaltered SeedSigner software.
+The *verify* command below, identifies *who exactly* created the signature file (.sig).
+The output of this verify command is the all-important *signers* fingerprint, and it is this fingerprint that you will visually compare to the fingerprint ID shown at Keybase.io/SeedSigner.
+If the ID matches, then you know it was seedsigner who signed it.
-The *verify* command below, identifies *who exactly* made the signature file.
-The output of this verify command is the all-important *signers* fingerprint, and it is this fingerprint that you will visually (and match!) to the fingerprint ID shown at Keybase.io/SeedSigner. If the ID matches, then you know it was seedsigner who signed it.
-
-(More specifically, the verify command determines *which* key pair already on your computer, signed the sha256.sig file. It does this comparing the file cryptographically to its unsigned equivalent (the .sha256 file).)
+(More specifically, the verify command determines *which* key pair already installed on your computer, signed the sha256.sig file. It does this cryptographically comparing the sha25.sig file to its unsigned equivalent (the .sha256 file).) using the public key already imported into your computer's keystore.
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
```
-**Note:** The `*`s in the command will auto-match to the version number in your current folder. It should be copied and pasted as-is.
+**Note:** The `*`'s in the command above are used to auto-fill the version numbers from your current folder, so it should be copied and pasted as-is.
The response you receive **must** include the phrase **"Good signature"**, like this:
>Good signature from "seedsigner
If the response displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-If you receive the warning message below, it can be safely ignored *because* you are going to be matching the fingerprint ID manually, to Keybase.io/seedsigner.
+If you receive the warning message below, it can be safely ignored *because* you are going to be matching the fingerprint ID now, to Keybase.io/seedsigner.
> gpg: WARNING: This key is not certified with a trusted signature!
> gpg: There is no indication that the signature belongs to the owner.
-If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID. you must now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner. If the fingerprint ID matches, then you have successfully verified that seedsigner signed the software you have just downloaded.
+
+If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID. You **must** now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner. If the fingerprint ID matches, then you have successfully verified that have received seedsigners genuine digital signature.
+
If it does not match perfectly, then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-The final verification step is to make sure that the other downloaded files (eg the files inside the zip file) were not altered or added to in any way. Even a single character being changed or removed, would show up here.
+### The final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to in any way. Even a single character being changed or removed, would show up here.
-**On Linux or OSX**
+**On Linux or OSX** run this command
```
shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
```
-**On Windows (Powershell)**
+**On Windows (inside Powershell)** run this command
```
CertUtil -hashfile seedsigner_0_*_*.img.zip SHA256 | findstr /v "hash"
```
@@ -167,11 +170,16 @@ The response must include the text **seedsigner_[VersionNumber].img.zip OK**, li
```
seedsigner_0_5_x.img.zip: OK
```
-**If you have received the OK message above then your verification has suceeded! - well done, the download files are now all confirmed as authentic and unaltered**!
+**If you have received the OK message above then your verification has suceeded! :) :) !! all the download files are now all confirmed as authentic and unaltered**!
If the result did not display "OK", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and their private key is not compromised or somehow being used by a malicious actor.
+Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and their private key is not compromised or somehow being used by a malicious actor.
+
+##Writing to your MicroSD card
+### Insert more here
+to be done by MarcG
+
---------------
# Enclosure Designs
From 1175ec4621c46cbcd6617f133e387cb850ccf2df Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Fri, 9 Dec 2022 19:17:13 -0800
Subject: [PATCH 06/41] Various Minor Language edits
---
README.md | 36 +++++++++++++++++++-----------------
1 file changed, 19 insertions(+), 17 deletions(-)
diff --git a/README.md b/README.md
index a7093816..13245592 100644
--- a/README.md
+++ b/README.md
@@ -90,42 +90,39 @@ Download these files to your computer:
2. seedsigner_0_5_x.img.zip.sha256
3. seedsigner_0_5_x.img.zip.sha256.sig
-Once the files have all finished downloading, follow the steps below to verify and to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can being using your Seedsinger!
+Once the files have all finished downloading, follow the steps below to verify, and to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can being using your Seedsigner!
**Note:** The version numbers of the latest files will be higher than this example, but the naming format will be the same.
-## Verifying that the downloaded files are authentic (optional but recommended!)
+## Verifying that the downloaded files are authentic (An optional but recommended step!)
You can quickly verify that the downloaded software is both authentic and unaltered, by following these instructions.
This step assumes you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
-Begin in the same folder where you have saved the download files.
-(Which will most likely be your Downloads folder.)
-
### Import the public key of the SeedSigner Project into your computer
The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
-The Keybase.io website service allows you to independently verify that the key is authentic and that it belongs to the organization it claims to represent. Keybase has checked it cryptographically and it has saved and matched in 3 separate online locations (On Twitter, on the Seedsigner.com website and lastly in the github.com/seedsigner software repository).
+The Keybase.io website service allows you to independently verify that the key is authentic and that it belongs to the organization it claims to represent. Keybase has checked it cryptographically and it has been saved and matched in 3 separate online locations already. These are: Twitter.com/seedsigner, on the Seedsigner.com website and lastly our software repository on Github github.com/seedsigner.
If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
-Now run this command (from inside the same folder that you saved the downloaded files into):
+To begin, run fetch-keys command shown below (from inside the *same folder* that you saved the downloaded files into).
+
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
-When the command completes successfully, it will display a numeric ID, as circled in red in the example below. We will use that numeric ID in the next step.
+When the command completes successfully, it will display a numeric ID, as circled in red in the example below. We will use that numeric ID in the subsequent steps. Please ignore the email address shown, because it is not part of the verification.

-### Verifying that your signature file is signed by the right person(s)
+### Verifying that the signature file is signed by the correct person(s)
-The *verify* command below, identifies *who exactly* created the signature file (.sig).
-The output of this verify command is the all-important *signers* fingerprint, and it is this fingerprint that you will visually compare to the fingerprint ID shown at Keybase.io/SeedSigner.
-If the ID matches, then you know it was seedsigner who signed it.
+The next command, which is the *verify* command, identifies *who exactly* created the signature file (.sig) you downloaded earlier.
+The output will display the all-important *signers* fingerprint, and it is this fingerprint ID which you must compare to keybase.io/seedsigner, yourself.
-(More specifically, the verify command determines *which* key pair already installed on your computer, signed the sha256.sig file. It does this cryptographically comparing the sha25.sig file to its unsigned equivalent (the .sha256 file).) using the public key already imported into your computer's keystore.
+(More specifically, the verify command determines *which* key pair already installed on your computer, actually signed the sha256.sig file. It does this by comparing cryptographically the sha25.sig file to its unsigned equivalent (the .sha256 file).), using the public key already imported into your computer.
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
@@ -140,21 +137,26 @@ The email address is JUST informational. Ignore it completely. *Only* the match
If the response displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-If you receive the warning message below, it can be safely ignored *because* you are going to be matching the fingerprint ID now, to Keybase.io/seedsigner.
+If you receive the warning message below, it can be safely ignored *because* you are going to be visually matching the fingerprint ID outputted to Keybase.io/seedsigner.
> gpg: WARNING: This key is not certified with a trusted signature!
> gpg: There is no indication that the signature belongs to the owner.
-If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID. You **must** now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner. If the fingerprint ID matches, then you have successfully verified that have received seedsigners genuine digital signature.
+If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID.
+You **must** now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner, yourself.
+Open the Keybase.io/SeedSigner. KeyBase.io/SeedSigner
+and now visually compare the fingerprint ID shown there to the Fingerprint ID outputted from the *verify* command.
+If they match exactly, then you have successfully confirmed that it was seedsigner who signed.
If it does not match perfectly, then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-### The final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to in any way. Even a single character being changed or removed, would show up here.
+### The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to, in any way.
+Even a single character being changed or removed, would show up here.
**On Linux or OSX** run this command
```
@@ -170,7 +172,7 @@ The response must include the text **seedsigner_[VersionNumber].img.zip OK**, li
```
seedsigner_0_5_x.img.zip: OK
```
-**If you have received the OK message above then your verification has suceeded! :) :) !! all the download files are now all confirmed as authentic and unaltered**!
+**If you have received the "OK" message above then your verification has suceeded! :) :) !! All the download files are now all confirmed as both authentic and unaltered**!
If the result did not display "OK", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
From d57ea8cba4442410c71eb29090132efccdb07bdd Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 11 Dec 2022 01:09:32 -0800
Subject: [PATCH 07/41] Add sample images to PubKey verification section
Clarifed shasum result about ignoring the warning about 4 improperly formatted lines
---
README.md | 19 ++++++++++++++-----
1 file changed, 14 insertions(+), 5 deletions(-)
diff --git a/README.md b/README.md
index 13245592..0b8c9316 100644
--- a/README.md
+++ b/README.md
@@ -142,6 +142,8 @@ If you receive the warning message below, it can be safely ignored *because* you
> gpg: WARNING: This key is not certified with a trusted signature!
> gpg: There is no indication that the signature belongs to the owner.
+
+
If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID.
@@ -149,8 +151,12 @@ You **must** now visually compare that ID to the fingerprint ID shown at Keybase
Open the Keybase.io/SeedSigner. KeyBase.io/SeedSigner
and now visually compare the fingerprint ID shown there to the Fingerprint ID outputted from the *verify* command.
-If they match exactly, then you have successfully confirmed that it was seedsigner who signed.
+
+
+
+If these 16 character fingerprint ID's match exactly, then you have successfully confirmed that it was seedsigner who signed!
+(The Fingerprint ID's are blurred out deliberately, to ensure you check them on *your* computer.)
If it does not match perfectly, then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
@@ -168,18 +174,21 @@ shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
CertUtil -hashfile seedsigner_0_*_*.img.zip SHA256 | findstr /v "hash"
```
-The response must include the text **seedsigner_[VersionNumber].img.zip OK**, like this:
+The response must include the text **seedsigner_[VersionNumber].img.zip: OK**, like this example:
```
seedsigner_0_5_x.img.zip: OK
+shasum: WARNING: 4 Lines are improperly formatted
```
-**If you have received the "OK" message above then your verification has suceeded! :) :) !! All the download files are now all confirmed as both authentic and unaltered**!
+**If you have received the "OK" message above, then your verification has suceeded! :) :) !! All the download files are now all confirmed as both authentic and unaltered**!
+The warning message about 4 lines being improperly formatted can be safely ignored.
+
+If the result shows "FAILED", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-If the result did not display "OK", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and their private key is not compromised or somehow being used by a malicious actor.
##Writing to your MicroSD card
-### Insert more here
+### Insert more instructions here
to be done by MarcG
---------------
From 85fae7bd1c02d4aa382ef675d168c662869aba66 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 11 Dec 2022 01:34:28 -0800
Subject: [PATCH 08/41] Formatting changes and updated verify Screenshots
---
README.md | 35 +++++++++++++++--------------------
1 file changed, 15 insertions(+), 20 deletions(-)
diff --git a/README.md b/README.md
index 0b8c9316..918dd347 100644
--- a/README.md
+++ b/README.md
@@ -113,7 +113,7 @@ To begin, run fetch-keys command shown below (from inside the *same folder* that
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
-When the command completes successfully, it will display a numeric ID, as circled in red in the example below. We will use that numeric ID in the subsequent steps. Please ignore the email address shown, because it is not part of the verification.
+When the command completes successfully, it will display a numeric ID, as circled in red in the example below. We will use that numeric ID in the subsequent steps. Please ignore the email address shown, because it is not part of the verification.

@@ -127,38 +127,33 @@ The output will display the all-important *signers* fingerprint, and it is this
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
```
-**Note:** The `*`'s in the command above are used to auto-fill the version numbers from your current folder, so it should be copied and pasted as-is.
+**Note:** The `*`'s in the command above are used to auto-fill the version from your current folder, so it should be copied and pasted as-is.
-The response you receive **must** include the phrase **"Good signature"**, like this:
+The output should appear like this:
+
+
->Good signature from "seedsigner
-If the response displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-
-If you receive the warning message below, it can be safely ignored *because* you are going to be visually matching the fingerprint ID outputted to Keybase.io/seedsigner.
+--- The response you receive **must** include the phrase **"Good signature"**, like this:
+This warning message can be safely ignored *because* you are still going to be visually comparing the fingerprint ID outputted against Keybase.io/seedsigner.
> gpg: WARNING: This key is not certified with a trusted signature!
> gpg: There is no indication that the signature belongs to the owner.
-
-
-
-
-If you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID.
+**If** you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID.
You **must** now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner, yourself.
+The email address is JUST informational. Ignore it completely. *Only* the matching fingerprints count.
Open the Keybase.io/SeedSigner. KeyBase.io/SeedSigner
and now visually compare the fingerprint ID shown there to the Fingerprint ID outputted from the *verify* command.
+
+
-
+If these fingerprint ID's match exactly, then you have successfully confirmed that it was seedsigner who signed! (Matching the last 16 characters is sufficient.)
-
-If these 16 character fingerprint ID's match exactly, then you have successfully confirmed that it was seedsigner who signed!
-(The Fingerprint ID's are blurred out deliberately, to ensure you check them on *your* computer.)
-If it does not match perfectly, then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-
+Note: We have blurred out the Fingerprint ID's deliberately, to ensure *you* match them up on *your* own computer.
+
+If they do not match exactly or your verify output displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
### The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to, in any way.
From 47fb9fe5daa28c6ac355916aecd43bb98ea144be Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 11 Dec 2022 19:18:06 -0800
Subject: [PATCH 09/41] Edits to the shasum command description
---
README.md | 4 ++--
1 file changed, 2 insertions(+), 2 deletions(-)
diff --git a/README.md b/README.md
index 918dd347..f507cc16 100644
--- a/README.md
+++ b/README.md
@@ -157,9 +157,9 @@ If they do not match exactly or your verify output displays "BAD signature", the
### The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to, in any way.
-Even a single character being changed or removed, would show up here.
+Even a single character being changed or removed, would be identified by the *shasum* command, which verifies (via file hashes) that not even a single character, has been changed, added or removed since original publication or during the download.
-**On Linux or OSX** run this command
+ **On Linux or OSX** run this command
```
shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
```
From b9649cba5bfda82a8606500c34c51bf553346620 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 11 Dec 2022 21:38:33 -0800
Subject: [PATCH 10/41] Minor Edits
---
README.md | 30 +++++++++++++++++-------------
1 file changed, 17 insertions(+), 13 deletions(-)
diff --git a/README.md b/README.md
index f507cc16..070182f5 100644
--- a/README.md
+++ b/README.md
@@ -90,25 +90,26 @@ Download these files to your computer:
2. seedsigner_0_5_x.img.zip.sha256
3. seedsigner_0_5_x.img.zip.sha256.sig
-Once the files have all finished downloading, follow the steps below to verify, and to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can being using your Seedsigner!
+Once the files have all finished downloading, follow the steps below to verify, and to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can begin using your Seedsigner!
**Note:** The version numbers of the latest files will be higher than this example, but the naming format will be the same.
-## Verifying that the downloaded files are authentic (An optional but recommended step!)
+## Verifying that the downloaded files are authentic (optional but highly recommended!)
+
You can quickly verify that the downloaded software is both authentic and unaltered, by following these instructions.
-This step assumes you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
+These next steps assume you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you also know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
-### Import the public key of the SeedSigner Project into your computer
+ ### 1. Import the public key of the SeedSigner Project into your computer
-The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
-The Keybase.io website service allows you to independently verify that the key is authentic and that it belongs to the organization it claims to represent. Keybase has checked it cryptographically and it has been saved and matched in 3 separate online locations already. These are: Twitter.com/seedsigner, on the Seedsigner.com website and lastly our software repository on Github github.com/seedsigner.
+ The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
+ The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. Keybase has checked it cryptographically and it has also been saved and matched in 3 separate online locations already. These are: Twitter.com/seedsigner, on the Seedsigner.com website and lastly our software repository on Github github.com/seedsigner. You can verify those yourself from keybase.io
If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
-To begin, run fetch-keys command shown below (from inside the *same folder* that you saved the downloaded files into).
+To begin, you will run the *fetch-keys* command as shown below (from inside the *same folder* that you saved the downloaded files into).
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
@@ -117,7 +118,7 @@ When the command completes successfully, it will display a numeric ID, as circle

-### Verifying that the signature file is signed by the correct person(s)
+### 2. Verifying that the signature file is signed by the correct person(s)
The next command, which is the *verify* command, identifies *who exactly* created the signature file (.sig) you downloaded earlier.
The output will display the all-important *signers* fingerprint, and it is this fingerprint ID which you must compare to keybase.io/seedsigner, yourself.
@@ -155,9 +156,10 @@ Note: We have blurred out the Fingerprint ID's deliberately, to ensure *you* mat
If they do not match exactly or your verify output displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
+
+### 3. The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to, in any way.
-### The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to, in any way.
-Even a single character being changed or removed, would be identified by the *shasum* command, which verifies (via file hashes) that not even a single character, has been changed, added or removed since original publication or during the download.
+Even a single character being changed or removed, would be identified by the *shasum* command, which verifies (via file hashes) that not even a single character, has been changed, added or removed since original publication or during the download.
**On Linux or OSX** run this command
```
@@ -181,10 +183,12 @@ If the result shows "FAILED", then you must stop here immediately. Do not contin
Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and their private key is not compromised or somehow being used by a malicious actor.
+
-##Writing to your MicroSD card
-### Insert more instructions here
-to be done by MarcG
+
+## Writing to your MicroSD card
+ Insert more instructions here
+ to be done by MarcG
---------------
From 76875f6e69d2d46c4b0c44d851d528558f823c2e Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 11 Dec 2022 22:34:50 -0800
Subject: [PATCH 11/41] Minor edits and clarifications.
---
README.md | 46 ++++++++++++++++++++++++----------------------
1 file changed, 24 insertions(+), 22 deletions(-)
diff --git a/README.md b/README.md
index 070182f5..f43a50c6 100644
--- a/README.md
+++ b/README.md
@@ -102,64 +102,66 @@ You can quickly verify that the downloaded software is both authentic and unalte
These next steps assume you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you also know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
- ### 1. Import the public key of the SeedSigner Project into your computer
+### 1. Import the public key of the SeedSigner project into your computer
- The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
- The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. Keybase has checked it cryptographically and it has also been saved and matched in 3 separate online locations already. These are: Twitter.com/seedsigner, on the Seedsigner.com website and lastly our software repository on Github github.com/seedsigner. You can verify those yourself from keybase.io
+The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
+
+The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. Keybase has checked the pubkey cryptographically when was saved in the 3 separate online locations. These are: on Twitter.com/seedsigner, on the website www.seedsigner.com , and on the software repository at Github github.com/seedsigner. You can verify those 3 Keys yourself, by clicking the 3 blue badges on keybase.io/seedsigner.
If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
-To begin, you will run the *fetch-keys* command as shown below (from inside the *same folder* that you saved the downloaded files into).
+To begin, you will run the *fetch-keys* command as shown below (run it from inside the *same folder* that you saved the downloaded files into).
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
-When the command completes successfully, it will display a numeric ID, as circled in red in the example below. We will use that numeric ID in the subsequent steps. Please ignore the email address shown, because it is not part of the verification.
+When the command completes successfully, it will show that this key was imported (or updated) successfully. A numeric ID, as circled in red in the example below is known as the keys fingerprint. Please ignore the email address shown, because it is not part of any verification.

### 2. Verifying that the signature file is signed by the correct person(s)
-The next command, which is the *verify* command, identifies *who exactly* created the signature file (.sig) you downloaded earlier.
+The 2nd command, is the *verify* command, which identifies *who* specifically created the signature file (.sig) you downloaded already.
The output will display the all-important *signers* fingerprint, and it is this fingerprint ID which you must compare to keybase.io/seedsigner, yourself.
-(More specifically, the verify command determines *which* key pair already installed on your computer, actually signed the sha256.sig file. It does this by comparing cryptographically the sha25.sig file to its unsigned equivalent (the .sha256 file).), using the public key already imported into your computer.
+(More specifically, the verify command determines *which* key pair of those already installed on your computer, actually signed the sha256.sig file. It does this by cryptographically comparing the sha25.sig file to its unsigned equivalent (the .sha256 file), with the public keys already imported into your computer.
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
```
**Note:** The `*`'s in the command above are used to auto-fill the version from your current folder, so it should be copied and pasted as-is.
-The output should appear like this:
+The response you receive should appear like this:

---- The response you receive **must** include the phrase **"Good signature"**, like this:
-
This warning message can be safely ignored *because* you are still going to be visually comparing the fingerprint ID outputted against Keybase.io/seedsigner.
> gpg: WARNING: This key is not certified with a trusted signature!
> gpg: There is no indication that the signature belongs to the owner.
-**If** you received the phase **"good Signature"**, then the last output line will display a fingerprint ID. That is the all-important *signers* fingerprint ID.
-You **must** now visually compare that ID to the fingerprint ID shown at Keybase.io/SeedSigner, yourself.
-The email address is JUST informational. Ignore it completely. *Only* the matching fingerprints count.
+**If** you received the phase **"good Signature"**, then the last output line will display a 16 character fingerprint ID.
+That is the all-important *signers* fingerprint ID.
+You **must** now visually compare that ID to the one shown at Keybase.io/SeedSigner, **yourself**.
+Any email address is JUST informational. Ignore it completely. *Only* the matching fingerprints count.
-Open the Keybase.io/SeedSigner. KeyBase.io/SeedSigner
-and now visually compare the fingerprint ID shown there to the Fingerprint ID outputted from the *verify* command.
+Open the website Keybase.io/SeedSigner. KeyBase.io/SeedSigner
+and visually compare the fingerprint ID shown there to the Fingerprint ID outputted by your *verify* command.
-
+
-If these fingerprint ID's match exactly, then you have successfully confirmed that it was seedsigner who signed! (Matching the last 16 characters is sufficient.)
+
+If these two fingerprint ID's match exactly, then you have successfully confirmed that it was seedsigner who signed! (Matching the last 16 characters is sufficient.)
Note: We have blurred out the Fingerprint ID's deliberately, to ensure *you* match them up on *your* own computer.
-If they do not match exactly or your verify output displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
+If they do not match exactly, or your verify output displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-### 3. The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file) were not altered or added to, in any way.
+### 3. Verifying that the software files were not tampered with
-Even a single character being changed or removed, would be identified by the *shasum* command, which verifies (via file hashes) that not even a single character, has been changed, added or removed since original publication or during the download.
+The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file), were not altered or added to in any way.
+The *shasum* command, verifies (via file hashes) that not even a single character, has been changed, added or removed since publication or during your download.
**On Linux or OSX** run this command
```
@@ -171,7 +173,7 @@ shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
CertUtil -hashfile seedsigner_0_*_*.img.zip SHA256 | findstr /v "hash"
```
-The response must include the text **seedsigner_[VersionNumber].img.zip: OK**, like this example:
+Allow about 30 seconds for the command to run, and then the response must include the text **seedsigner_[VersionNumber].img.zip: OK**, like this example:
```
seedsigner_0_5_x.img.zip: OK
shasum: WARNING: 4 Lines are improperly formatted
@@ -186,7 +188,7 @@ Please recognize that this process can only validate the software to the extent
-## Writing to your MicroSD card
+## Writing the software to your MicroSD card
Insert more instructions here
to be done by MarcG
From d2a657f2d43c6e77e9c48cb1f859e8f4984a5f00 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Mon, 12 Dec 2022 00:03:33 -0800
Subject: [PATCH 12/41] Various edits B4 upstream submission
After a long hiatus, I have finally completed my proposed changes to the software verification section of our readme.
The verification focuses on keybase.io now storing and verifying the 3 online properties (seedsigner.com, twitter.com/seedsigner and github.com/seedsigner)
This makes the key more secure, easier to import and generally less hassle. its also revokable.
There is more detail about how/why in the expand blocks, but It was suggested to me to keep the instructions straightforward (ie do this and now do that) , so I have reduced focus much on the why.
However, some basic "why & how" has also been placed in new collapsible sections, at the end of each step.
Later on, I want to add color to the collapse sections so that they show a natural boundary, but so far that markdown code is elusive to me. ;)
Done is better than perfect....
The same for getting my external links to open in a new tab/window. sigh. Markdown is ... well....tricky.
I can make the screenshots smaller. please comment on their size.
The Verification is done in 3 steps:
1. import the public key
2. Verify its the correct key by verying it and then comparing the Key ID to Keybase.io/seedsigner. If it matches, then its the real seedsigner project person that signed.
this is arguablly the most critical step of verifying and hence we ask the user to check for themselves that the key ID from verify is the same as on keybase.io. Hence the Key ID's are blurred in the screenshots. We dont want the user to compare the screenshots to each other. we want them to compare their result to their browser.
3. Verify that the other files (at this stage just the .zip file) are also not altered. This does a comparision of the various files actual and expected hashes.
If all is well here, then tell the user about their success :).
Explain the warnings, which ones are benign, and what to do if verification fails.
Lastly, "Write the software to the MicroSD' section -
I have got draft text for this, but havent published it yet.
The verify PR is big enough !!
Please review for my PR flow and clarity, I do still want to improve the formatting, but wanted to get everyone's thoughts before messing with the detailed formatting and line breaks, which are especially painful!
FYI - I have done my screenshots using layers, so it easy to edit in the future. I think they
---
README.md | 45 ++++++++++++++++++++++++++++++++-------------
1 file changed, 32 insertions(+), 13 deletions(-)
diff --git a/README.md b/README.md
index f43a50c6..f3892870 100644
--- a/README.md
+++ b/README.md
@@ -105,27 +105,35 @@ These next steps assume you are running the commands from a computer where both
### 1. Import the public key of the SeedSigner project into your computer
The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*.
-
-The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. Keybase has checked the pubkey cryptographically when was saved in the 3 separate online locations. These are: on Twitter.com/seedsigner, on the website www.seedsigner.com , and on the software repository at Github github.com/seedsigner. You can verify those 3 Keys yourself, by clicking the 3 blue badges on keybase.io/seedsigner.
-
-If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
To begin, you will run the *fetch-keys* command as shown below (run it from inside the *same folder* that you saved the downloaded files into).
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
-When the command completes successfully, it will show that this key was imported (or updated) successfully. A numeric ID, as circled in red in the example below is known as the keys fingerprint. Please ignore the email address shown, because it is not part of any verification.
+When the command completes successfully, it will show that this key was either imported or updated from Keybase.io. A numeric ID, as circled in red in the example below is known as the keys fingerprint. Please ignore the email address shown, because it is not part of any verification.

+Learn more about how keybase.io helps you check that someone is who they say they are
+
+
+
### 2. Verifying that the signature file is signed by the correct person(s)
The 2nd command, is the *verify* command, which identifies *who* specifically created the signature file (.sig) you downloaded already.
The output will display the all-important *signers* fingerprint, and it is this fingerprint ID which you must compare to keybase.io/seedsigner, yourself.
-(More specifically, the verify command determines *which* key pair of those already installed on your computer, actually signed the sha256.sig file. It does this by cryptographically comparing the sha25.sig file to its unsigned equivalent (the .sha256 file), with the public keys already imported into your computer.
-
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
```
@@ -157,8 +165,18 @@ Note: We have blurred out the Fingerprint ID's deliberately, to ensure *you* mat
If they do not match exactly, or your verify output displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
-
-### 3. Verifying that the software files were not tampered with
+
+Learn more about signature file verification
+
+
+### 3. Verifying that the software files were not tampered with
The 3rd and final verification step is to make sure that all the other downloaded files (eg the files inside the zip file), were not altered or added to in any way.
The *shasum* command, verifies (via file hashes) that not even a single character, has been changed, added or removed since publication or during your download.
@@ -178,9 +196,10 @@ Allow about 30 seconds for the command to run, and then the response must includ
seedsigner_0_5_x.img.zip: OK
shasum: WARNING: 4 Lines are improperly formatted
```
-**If you have received the "OK" message above, then your verification has suceeded! :) :) !! All the download files are now all confirmed as both authentic and unaltered**!
-The warning message about 4 lines being improperly formatted can be safely ignored.
+**If you have received the "OK" message above, then your verification has suceeded! 😄😄 !! 👍 All the download files have now been confirmed as both authentic and unaltered**!
+The warning message about 4 lines being improperly formatted can be safely ignored.
+
If the result shows "FAILED", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram address above.
@@ -189,8 +208,8 @@ Please recognize that this process can only validate the software to the extent
## Writing the software to your MicroSD card
- Insert more instructions here
- to be done by MarcG
+ Insert more instructions here.
+ (to be done by MarcG)
---------------
From 923ce08f4992a0943646c259c2a384530d490b70 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Mon, 12 Dec 2022 00:06:46 -0800
Subject: [PATCH 13/41] Various edits B4 Upstream commit
---
README.md | 2 +-
1 file changed, 1 insertion(+), 1 deletion(-)
diff --git a/README.md b/README.md
index f3892870..1d5addcc 100644
--- a/README.md
+++ b/README.md
@@ -174,7 +174,7 @@ More specifically, the verify command determines *which* key pair of those alrea
- The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. - Keybase has checked the pubkey cryptographically when it was saved in the 3 separate online locations. These are: on www.twitter.com/seedsigner, on the website www.seedsigner.com , and in the software repository at Github www.github.com/seedsigner. - You can verify those 3 separate Key locations yourself, by clicking the 3 blue badges on www.keybase.io/seedsigner. (The Twittter blue badge one is the most human-readble.) + The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. + Keybase has already checked the three pubkey files cryptographically when they were saved, however, if you would like to, you can further verify the three Key publications, either: + + - via Keybase: By clicking on any of the three blue badges at www.keybase.io/seedsigner. (The blue badge for the publication on Twitter is in the most human-readable form), or, + - without using keybase at all: By using these 3 links directly: [Twitter](https://twitter.com/seedsigner/status/1530555252373704707) , [Github](https://gist.github.com/SeedSigner/5936fa1219b07e28a3672385b605b5d2) and [Seedsigner.com](https://seedsigner.com/keybase.txt). This method can be used if you would like to make an even deeper, independent inspection without relying on Keybase at all, or if the Keybase.io site is no longer valid or it is removed entirely. + If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window)
From 3c43ea3a291b5d73d8f374430e00e49973937d9d Mon Sep 17 00:00:00 2001 From: Marc G <91296549+Marc-Gee@users.noreply.github.com> Date: Sun, 29 Jan 2023 12:07:04 +0000 Subject: [PATCH 15/41] Updates to shorten the verification instructions --- README.md | 82 +++++++++++++++++++++++++++---------------------------- 1 file changed, 40 insertions(+), 42 deletions(-) diff --git a/README.md b/README.md index eaf01cfe..e46d1b0c 100644 --- a/README.md +++ b/README.md @@ -102,30 +102,27 @@ You can quickly verify that the downloaded software is both authentic and unalte These next steps assume you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you also know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal). -### 1. Import the public key of the SeedSigner project into your computer +### 1. Import the public key of the SeedSigner project into your computer: -The *fetch-keys* command below will import the SeedSigner projects public key from a popular online keyserver called *Keybase.io*, into your computers *keychain*. +Run the *fetch-keys* command to import the SeedSigner projects public key from the popular online keyserver called *Keybase.io*, into your computers *keychain*. -To begin, you will run the *fetch-keys* command as shown below (run it from inside the *same folder* that you saved the downloaded files into). ``` gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc ``` -When the command completes successfully, it will show that this key was either imported or updated from Keybase.io. -A numeric ID, as circled in red in the example below is known as the key's fingerprint. Please ignore the email address shown, because it is not part of any verification. +When the command completes successfully, it should display that a key was either imported or updated. Ignore any email address shown. - The Keybase.io website allows you to independently verify that the public key provided is authentic and that it belongs to the organization it claims to represent. - Keybase has already checked the three pubkey files cryptographically when they were saved, however, if you would like to, you can further verify the three Key publications, either: +Keybase.io allows you to independently verify that the public key saved on Keybase.io, is both authentic and that it belongs to the organization it claims to represent. + Keybase has already checked the three pubkey files cryptographically when they were saved. However, if you like, you can further verify the Key publications, either : - - via Keybase: By clicking on any of the three blue badges at www.keybase.io/seedsigner. (The blue badge for the publication on Twitter is in the most human-readable form), or, - - without using keybase at all: By using these 3 links directly: [Twitter](https://twitter.com/seedsigner/status/1530555252373704707) , [Github](https://gist.github.com/SeedSigner/5936fa1219b07e28a3672385b605b5d2) and [Seedsigner.com](https://seedsigner.com/keybase.txt). This method can be used if you would like to make an even deeper, independent inspection without relying on Keybase at all, or if the Keybase.io site is no longer valid or it is removed entirely. + - *via Keybase*: By clicking on any of the three blue badges at [Keybase.io/seedsigner](www.keybase.io/seedsigner) to see what was published there. (The blue badge for the publication on Twitter is in the most human-readable form and it is also bi-directional), or, + - *without keybase*: By using these 3 links directly: [Twitter](https://twitter.com/seedsigner/status/1530555252373704707) , [Github](https://gist.github.com/SeedSigner/5936fa1219b07e28a3672385b605b5d2) and [Seedsigner.com](https://seedsigner.com/keybase.txt). This method can be used if you would like to make an even deeper, independent inspection without relying on Keybase at all, or if the Keybase.io site is no longer valid or it is removed entirely. - - If you need more information, please open the website KeyBase.io/SeedSigner (it opens in a separate tab or window) +Once you have used one of these methods, you will know if the Public Key stored on Keybase, is genuinely from the SeedSinger Project or not.
Since you are going to now match the outputted fingerprint ID against Keybase.io/seedsigner, you can ignore this warning message: + +``` +> WARNING: This key is not certified with a trusted signature! +> There is no indication that the signature belongs to the owner. + ``` -This warning message can be safely ignored *because* you are still going to be visually comparing the fingerprint ID outputted against Keybase.io/seedsigner. -> gpg: WARNING: This key is not certified with a trusted signature! -> gpg: There is no indication that the signature belongs to the owner. - -**If** you received the phase **"good Signature"**, then the last output line will display a 16 character fingerprint ID. -That is the all-important *signers* fingerprint ID. -You **must** now visually compare that ID to the one shown at Keybase.io/SeedSigner, **yourself**. -Any email address is JUST informational. Ignore it completely. *Only* the matching fingerprints count. +
+-More specifically, the verify command determines *which* key pair of those already installed on your computer, actually signed the sha256.sig file. It does this by cryptographically comparing the sha25.sig file to its unsigned equivalent (the .sha256 file), looping through the public keys already imported into your computer. whichever installed/imported key is able to perform the comparision successfully, then that is the pubkey of the keypair that was used! +More specifically, the verify command determines *which* key pair of those already installed on your computer, actually signed the sha256.sig file. It does this by cryptographically comparing the sha256.sig file to its unsigned equivalent (the .sha256 file), while looping through the public keys already imported into your computer. Whomever's pre-imported Pubkey is able to perform the comparison successfully, is the Pubkey of the keypair used in the signing process. That 'winning' Public key must match the Public Key we have previously found, and verified as genuine on keybase.io.
Since you are going to now match the outputted fingerprint ID against Keybase.io/seedsigner, you can ignore this warning message:
@@ -161,7 +161,8 @@ Ignore any email addresses. *Only* matching fingerprints count here.
Now open the website [Keybase.io/seedsigner](www.keybase.io/seedsigner) and compare the 16 character fingerprint ID (circled red in the screenshot below), to the *rightmost* 16 characters from your *verify* command. **Make sure that they match exactly**.
Since you are going to now match the outputted fingerprint ID against Keybase.io/seedsigner, you can ignore this warning message:
+ Since you are going to now match the outputted fingerprint ID against the source proofs at Keybase.io/seedsigner, you can ignore this warning message:
```
> WARNING: This key is not certified with a trusted signature!
> There is no indication that the signature belongs to the owner.
```
-
-
-Keybase.io allows you to independently verify that the public key saved on Keybase.io, is both authentic and that it belongs to the organization it claims to represent.
- Keybase has already checked the three pubkey files cryptographically when they were saved. However, if you like, you can further verify the Key publications, either :
-
- - *via Keybase*: By clicking on any of the three blue badges at [Keybase.io/seedsigner](www.keybase.io/seedsigner) to see what was published there. (The blue badge for the publication on Twitter is in the most human-readable form and it is also bi-directional), or,
- - *without keybase*: By using these 3 links directly: [Twitter](https://twitter.com/seedsigner/status/1530555252373704707) , [Github](https://gist.github.com/SeedSigner/5936fa1219b07e28a3672385b605b5d2) and [Seedsigner.com](https://seedsigner.com/keybase.txt). This method can be used if you would like to make an even deeper, independent inspection without relying on Keybase at all, or if the Keybase.io site is no longer valid or it is removed entirely.
-
-Once you have used one of these methods, you will know if the Public Key stored on Keybase, is genuinely from the SeedSinger Project or not.
- Since you are going to now match the outputted fingerprint ID against the source proofs at Keybase.io/seedsigner, you can ignore this warning message:
+ Since you are about to match the outputted fingerprint/ID against the proofs at Keybase.io/seedsigner, and thereby confirm who the pubkey really belongs to-, you can safely ignore this warning message:
```
> WARNING: This key is not certified with a trusted signature!
@@ -157,30 +139,49 @@ On the *last* output line, look at the *rightmost* 16 characters (circled in red
+The verify command will attempt to decrypt the signature file (sha256.sig) by trying each public key already imported into your computer. If the public key we just imported (via fetch-keys), manages to: (a) successfully decrypt the .sig file , and (b), that result matches exactly to the clear-text equivalent (.sha256) of the .sig file, then its "a good signature"!
+
+Crucially, we must still manually check who *exactly* owns the Key ID which gave us that "Good signature". Thats what the warning message means- Who does the matching key really belong to? We will start by looking at keybase.io to see if it is "The Seedsigner project"'s public Key or not.
+Note that it is the file hashes of .sig and .sha256 that *verify* compares, not their raw contents.
+
+
+Keybase.io allows you to independently verify that the public key saved on Keybase.io, is both authentic and that it belongs to the organization it claims to represent.
+ Keybase has already checked the three pubkey file locations cryptographically when they were saved there. You can further verify the key publications if you would like:
+
+ - *via Keybase*: By clicking on any of the three blue badges to see that the "proof" was published at that location. (The blue badge marked as tweet, is in the most human-readable form and it is also a bi-directional link on Twitter)
+or,
+ - *without keybase (out-of-band)*: By using these 3 links directly: [Twitter](https://twitter.com/seedsigner/status/1530555252373704707), [Github](https://gist.github.com/SeedSigner/5936fa1219b07e28a3672385b605b5d2) and [Seedsigner.com](https://seedsigner.com/keybase.txt). This method can be used if you would like to make an even deeper, independent inspection without relying on Keybase at all, or if the Keybase.io site is no longer valid or it is removed entirely.
-More specifically, the verify command determines *which* key pair of those already installed on your computer, actually signed the sha256.sig file. It does this by cryptographically comparing the sha256.sig file to its unsigned equivalent (the .sha256 file), while looping through the public keys already imported into your computer. Whomever's pre-imported Pubkey is able to perform the comparison successfully, is the Pubkey of the keypair used in the signing process. That 'winning' Public key must match the Public Key we have previously found, and verified as genuine on keybase.io.
-
+Once you have used one of these methods, you will know if the Public Key stored on Keybase, is genuinely from the SeedSinger Project or not.
>TWDY+zM#c7CulIXfFCI}bltg`5NY61c?9%f|(l
zBiAG6W@jho;9xfp5y7-@Fn^ed{9iwqXk2Xne1?>TnWMRdnu#;S1$d&QqrDr%!G)X~
ztmbTCZe!-^=uFPeAtC~nv9Wixa0biRo48v1aSK>pN>4~qQbLN2pF@UCf>)Z8lS`6c
zoQ;EnOOl6Ef=8N*Q(Q_!NL-v#Qc{Lnnn#j@pP!dYTAZ6*lAA|{U6PlRO@fn`O~e2!
z?_h4>sRszo$xY79NzVRo#?q0Tod;N@I#|iV!OGPd5SRU7P40h)$_-X`baW+W=leZG
z15gn;Hy8M&my-qfmAZu`SX+;s{9z^$5f@iy3lj(?n)QOIsk!lEV`EceV*vz8qT3E?
zln>@@*iRRcEr&p{*PWDZ#%B&}&B EI60MotDlBHAa;EZQ?O&$T1%sr#mPU#D3lP
zVqz$Xo!i5Qg1Y5s?>X5PZm_8DIXOUxgdm$50(nd{K;?fv@lWNuxSBY-dOBNJVxqBO
zqS4SutIA-a{lg%bXx!}oG{xWP7|;S>`ae~`$@O4-E^e>}IWNz@h-PeTY-w!#%fi^g
z_%WKvV{ #*ntOLHY}qhtWqH}*mip|RZt6+I_bqP-e~ogi
zPNYX`d*s}m2D&Ak6U;!}QgmVGn~R-1Qxc-HK`ma7omMKZd)Tp7n2v0Ocs^$DipVAi
zD3=thq56%Vi!`upcJeb8tf%AGg-n$vN5+;M+vu-*911t4I3+K#??2H`JUQgn+i|&h
zzA;l~Itt$1wSo>FbUocmgKf9I(Na1)if>iAmwnQX4r_buowJc3U-d2eF_s%cIUprD
zO)UT0SsZ>2Zu+!3yT)fZcB|>I!k_EV;3yBU1Ak@h#4tz4w3q1mPPi}a%TUzAuql1G
zr}=`0%PlRjf8zxqD_s#r2rsB1mOELN?y@1!;ChgvyjEL-bkm`P**_5<%<1pp}$dM&eMkr0FUL_&s(>EQV
zuA!9yBZw&}_4iZG>#3hsQ)Z*E_Rw?2hFi{Pb#I5v{A1it=LA>U6tLN-65}#gM?{HX
zawSQ2%swvWv7btkT$tlr`c^%P_z^*w8U^JBYy)XBNaZKsZpUQw7+!~x_g^b!Q)OK(
zJQn$M71o8CrCSQny`AILk>|Oicxn3MNY4gtu&%zf+p0B0*}+40_^Nc1Vh5EOwrCS+
za!6De2wgYE>#06g;CWu>wn4)_I2j4X(O`La#4V?sPe$SvAJT-5BX-}66%a7vEFBOX
z1Ru@`bW`Y_U&X$F@4m)YLnLmhIAf9i!iTxemCIC)-x13SNzv-AxgX0uTrsi0KVbaX
zyJFX-az9M^`H^$V!cV<~Bm4`nfiTa<8%vmIYVVsSHN8~p;N ~7(;bq+J+H@`YWF2Q&x6JqfgjX%;nD2
zTqPK~o9PJ?kYaE?s#gVzls_>sI*7wH*1PiTAP`yL@9*S!D&e=HQbWwNKqubySv)Dk
zlsMYvRemSGZL+^fppeZw^Un>HALD9mMoVop )17Ef;gijj47noHT;%agU5J3K%_Qfu)9fey`3v9PW@2HF8b
ze-tFcBIKi|r&l||*+zkCiVhm30Wi$1Ys(u*NEI;)$;+c@GeibaD+;v=oj>OrF7e20
zIIsB%WGEnvlzUR(!rR;74ZjztwgsZUo2HOs+YMwEdJEYc2I@%r>4u}}BQwhj?E59r
z8>^uEJy`nzkSvn9yc7;Z-fnYSC(#;s8>|=tH3wL~A?xA-14c^+ 8^q-W;o;$vy37-=
z-y{XA72W+tFTo AB8FQJhUS3I*R-Tn(0{raA~$#= w
ztrVr_7UiWdL|1uM@t_7)`aB+i%!(&!y;kKVZ_y&;&h*0WsP8xQ;igt1zk(2v
-
+
+
If the two fingerprint ID's match exactly, then you have successfully confirmed that your .sig file is authentic!
From 615460736c65f68b55f5a2ff243cd9ca0b03ae74 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 29 Jan 2023 08:16:05 -0800
Subject: [PATCH 17/41] Improved Screenshots
(nicer masking in the image)
---
README.md | 12 +++++-------
1 file changed, 5 insertions(+), 7 deletions(-)
diff --git a/README.md b/README.md
index 0cc4f43b..a295851c 100644
--- a/README.md
+++ b/README.md
@@ -142,19 +142,17 @@ gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
When the command completes successfully, it should look like this:
-
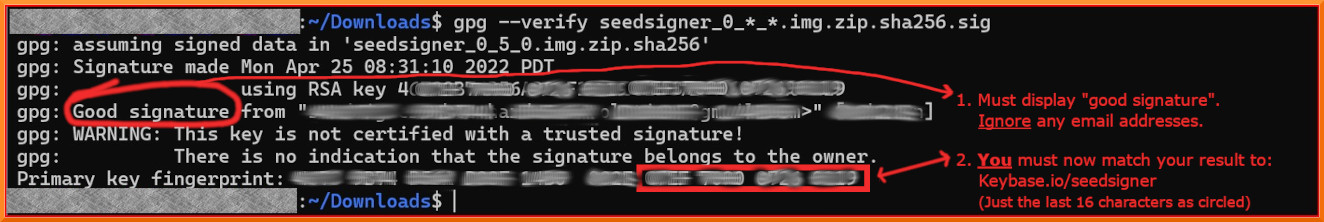
-It must show "**good** signature". Ignore any email addresses. *Only* matching fingerprints count here.
+
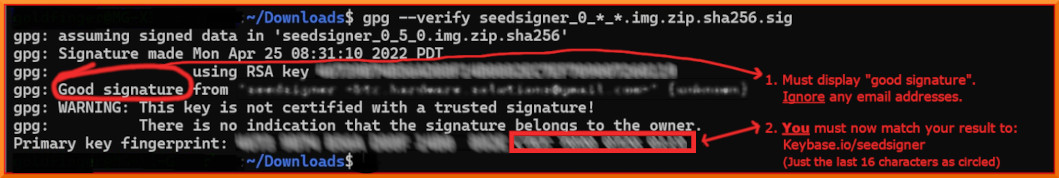
+It must display "**Good** signature". Ignore any email addresses. *Only* matching fingerprints count here. Stop here immediately if it displays "*Bad signature*"!
On the *last* output line, look at the *rightmost* 16 characters (circled in red in the picture above). That is *who* made the signature file (.sig).
- About warning messages:
- About the warning message:
+
@@ -167,7 +165,7 @@ Now open the website [Keybase.io/seedsigner](www.keybase.io/seedsigner) and comp
If the two fingerprint ID's match exactly, then you have successfully confirmed that your .sig file is authentic!
-If they do ***not match exactly***, or your verify command displays "BAD signature", then you must stop here immediately. Do not continue. Contact us for assistance in the Telegram group address above.
+If they do ***not match exactly***, or your verify command displayed "Bad signature", then you must stop here immediately. Do not continue. Contact us for assistance in the Telegram group address above.
Learn more about signature file verification
From b04383d087aed29462232f4334e1f2d0e8621be2 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Sun, 29 Jan 2023 20:02:19 +0000
Subject: [PATCH 18/41] Verification: Shortening, reordering & clarify
---
README.md | 96 +++++++++++++++++++++++++++++--------------------------
1 file changed, 50 insertions(+), 46 deletions(-)
diff --git a/README.md b/README.md
index a295851c..ec5b3313 100644
--- a/README.md
+++ b/README.md
@@ -90,64 +90,46 @@ Download these files to your computer:
2. seedsigner_0_5_x.img.zip.sha256
3. seedsigner_0_5_x.img.zip.sha256.sig
-Once the files have all finished downloading, follow the steps below to verify, and to write the software onto a MicroSD card. Then insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can begin using your Seedsigner!
-
**Note:** The version numbers of the latest files will be higher than this example, but the naming format will be the same.
+Once the files have all finished downloading, follow the steps below to verify them, and then to write the software onto a MicroSD card. Insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can begin using your Seedsigner!
+
+
## Verifying that the downloaded files are authentic (optional but highly recommended!)
-You can quickly verify that the downloaded software is both authentic and unaltered, by following these instructions.
-
-These next steps assume you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you also know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
+You can quickly verify that the software you just downloaded is both authentic and unaltered, by following these instructions.
+We assume you are running the commands from a computer where both [GPG](https://gnupg.org/download/index.html) and [shasum](https://command-not-found.com/shasum) are already installed, and that you also know [how to navigate on a terminal](https://terminalcheatsheet.com/guides/navigate-terminal).
-### 1. Import the public key of the SeedSigner project into your computer:
+### Step 1. Verify that the signature (.sig) file is genuine:
-Run the *fetch-keys* command to import the SeedSigner projects public key from the popular online keyserver called *Keybase.io*, into your computers *keychain*.
+Run GPG's *fetch-keys* command to import the SeedSigner projects public key from the popular online keyserver called *Keybase.io*, into your computers *keychain*.
```
gpg --fetch-keys https://keybase.io/SeedSigner/pgp_keys.asc
```
-When the command completes successfully, it should display that a key was either imported or updated. Ignore any email address shown.
+The result should confirm that 1 key was *either* imported or updated. *Ignore* any key ID's or email addresses shown.

-Learn more about how keybase.io helps you check that someone is who they say they are
-
-
-
-### 2. Checking that the *signature file* is genuinely from the SeedSigner Project:
-
-Running this *verify* command, will determine *who* created the signature file (.sig) you downloaded already.
-The output will display the all-important *signers* fingerprint, and it is this fingerprint ID which you will want to match to keybase, by yourself.
-
+Next, you will run the *verify* command on the signature (.sig) file. (*Verify* must be run from inside the same folder that you downloaded the files into earlier. The `*`'s in this command will auto-fill the version from your current folder, so it should be copied and pasted as-is.)
```
gpg --verify seedsigner_0_*_*.img.zip.sha256.sig
```
-**Note:** *Verify* must be run from inside the *same folder* that you downloaded the files into. The `*`'s in the command will auto-fill the version from your current folder, so it should be copied and pasted as-is.
-When the command completes successfully, it should look like this:
+When the verify command completes successfully, it should display output like this:

-It must display "**Good** signature". Ignore any email addresses. *Only* matching fingerprints count here. Stop here immediately if it displays "*Bad signature*"!
+The result must display "**Good signature**". Ignore any email addresses - *only* matching Key fingerprints count here. Stop immediately if it displays "*Bad signature*"!
-On the *last* output line, look at the *rightmost* 16 characters (circled in red in the picture above). That is *who* made the signature file (.sig).
+
+On the *last* output line, look at your *rightmost* 16 characters (the 4 blocks of 4).
+**Crucially, we must now check WHO that Primary key fingerprint /ID belongs to.** We will start by looking at Keybase.io to see if it is the *Seedsigner project* 's public key or not.
+
About the warning message:
-
-Now open the website [Keybase.io/seedsigner](www.keybase.io/seedsigner) and compare the 16 character fingerprint ID (circled red in the screenshot below), to the *rightmost* 16 characters from your *verify* command. **Make sure that they match exactly**.
+ More about how the verify command works:
+
+
+Now to determine ***who*** the Public key ID belongs to: Goto [Keybase.io/seedsigner](www.keybase.io/seedsigner)
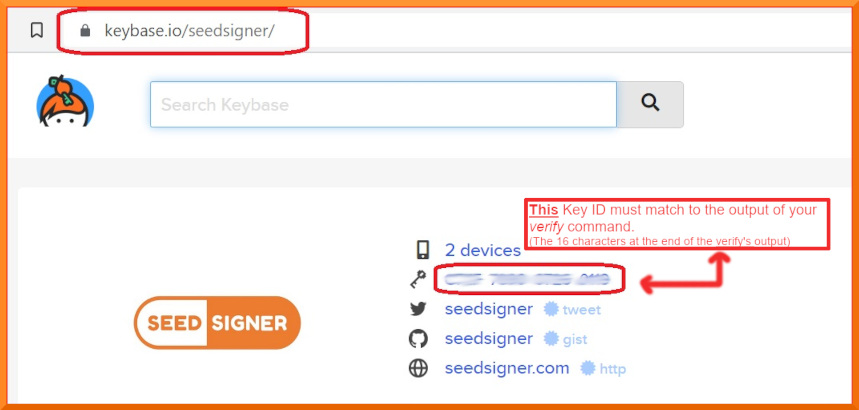
-If the two fingerprint ID's match exactly, then you have successfully confirmed that your .sig file is authentic!
+**You must now *manually* compare: The 16 character fingerprint ID (as circled in red above) to, those *rightmost* 16 characters from your *verify* command.**
+
+**If they match exactly, then you have successfully confirmed that your .sig file is authentically from the Seedsigner Project!**
-If they do ***not match exactly***, or your verify command displayed "Bad signature", then you must stop here immediately. Do not continue. Contact us for assistance in the Telegram group address above.
-
-Learn more about signature file verification
+Learn more about how keybase.io helps you check that someone (online) is who they say they are:
+
+If the two ID's do *not* match, then you must stop here immediately. Do not continue. Contact us for assistance in the Telegram group address above.
-### 3. Verifying that the *software files* are genuine
+### 2. Verifying that the *software images/binaries* are genuine
-Running the *shasum* command, is the final verification step and will confirm (via file hashing) that the software code (ie the binary files inside the zip file), were not altered, or added to, since publication or during your download. (Not by even one single character!)
+Now that you have confirmed that you do have the real Seedsigner Project's Public Key (ie the 16 characters match) - you can return to your terminal window. Running the the *shasum* command, is the final verification step and will confirm (via file hashing) that the software code/image files (ie the binary files inside the zip file), were also not altered since publication, or even during your download process.
**On Linux or OSX:** Run this command
```
@@ -191,21 +192,24 @@ shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
```
CertUtil -hashfile seedsigner_0_*_*.img.zip SHA256 | findstr /v "hash"
```
+
-Wait about 30 seconds for the command to complete
+Wait about 30 seconds for the command to complete, and it should display:
```
seedsigner_0_5_x.img.zip: OK
shasum: WARNING: 4 Lines are improperly formatted
```
-**If you receive the "OK" message** for the **seedsigner_[VersionNumber].img.zip file**, as shown above, then your verification is fully complete!
-**All of your downloaded files have now been confirmed as both authentic and unaltered!** 😄😄 !!
+**If you receive the "OK" message** for your **seedsigner_[x.x.x.VersionNumber].img.zip file**, as shown above, then your verification is fully complete!
+**All of your downloaded files have now been confirmed as both authentic and unaltered!** You can proceed to create/write your MicroSD card😄😄 !!
The warning message describing '4 lines being improperly formatted' can be safely ignored.
If your file result shows "FAILED", then you must stop here immediately. Do not continue. Contact us for assistance at the Telegram group address above.
+
Please recognize that this process can only validate the software to the extent that the entity that first published the key is an honest actor, and their private key is not compromised or somehow being used by a malicious actor.
+
## Writing the software to your MicroSD card
From a136a863552f9e1b0ff010d8036435e0d9aadc87 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Mon, 30 Jan 2023 15:52:52 -0800
Subject: [PATCH 19/41] Fix Spelling, grammar and shasum command
Spelling, grammar edits were made, - as suggested by the reviewers comments.
Additionally: 1) the Windows certutil (aka shasum) command for windows was clarified.
2) the shasum command on osX and Linux now includes the ignore-missing flag for compatibility with the expected new 0.5.2 shasum file format. The 0.5.2 shasum file will include hashes for multiple binaries now , but the user will likely only be checking one single binary. hence we tell shasum command to skip any missing files and to not report "missing files" error.
---
README.md | 9 +++++----
1 file changed, 5 insertions(+), 4 deletions(-)
diff --git a/README.md b/README.md
index ec5b3313..6c948301 100644
--- a/README.md
+++ b/README.md
@@ -91,7 +91,7 @@ Download these files to your computer:
3. seedsigner_0_5_x.img.zip.sha256.sig
**Note:** The version numbers of the latest files will be higher than this example, but the naming format will be the same.
-Once the files have all finished downloading, follow the steps below to verify them, and then to write the software onto a MicroSD card. Insert the MicroSD into your assembled hardware and turn on the USB power. Allow about 45 seconds for our logo to appear, and then you can begin using your Seedsigner!
+Once the files have all finished downloading, follow the steps below to verify the download before continuing on to write the software onto a MicroSD card. Next, insert the MicroSD into your assembled hardware and connect the USB power. Allow about 45 seconds for our logo to appear, and then you can begin using your Seedsigner!
@@ -179,20 +179,21 @@ If the two ID's do *not* match, then you must stop here immediately. Do not cont
-### 2. Verifying that the *software images/binaries* are genuine
+### Step 2. Verifying that the *software images/binaries* are genuine
Now that you have confirmed that you do have the real Seedsigner Project's Public Key (ie the 16 characters match) - you can return to your terminal window. Running the the *shasum* command, is the final verification step and will confirm (via file hashing) that the software code/image files (ie the binary files inside the zip file), were also not altered since publication, or even during your download process.
**On Linux or OSX:** Run this command
```
-shasum -a 256 -c seedsigner_0_*_*.img.zip.sha256
+shasum -a 256 --ignore-missing -check seedsigner_0_*_*.img.zip.sha256
```
**On Windows (inside Powershell):** Run this command
```
CertUtil -hashfile seedsigner_0_*_*.img.zip SHA256 | findstr /v "hash"
```
-
+On Windows, you must manually compare the above resulting hash value to the corresponding hash value shown inside the .SHA256 cleartext file.
+
Wait about 30 seconds for the command to complete, and it should display:
```
From e1090ba0c5d4ef525900462fded4b45a29842d0b Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Tue, 31 Jan 2023 05:21:38 -0800
Subject: [PATCH 20/41] Fix SHASUM option flag typo --check
---
README.md | 2 +-
1 file changed, 1 insertion(+), 1 deletion(-)
diff --git a/README.md b/README.md
index 6c948301..de7e54a5 100644
--- a/README.md
+++ b/README.md
@@ -185,7 +185,7 @@ Now that you have confirmed that you do have the real Seedsigner Project's Publi
**On Linux or OSX:** Run this command
```
-shasum -a 256 --ignore-missing -check seedsigner_0_*_*.img.zip.sha256
+shasum -a 256 --ignore-missing --check seedsigner_0_*_*.img.zip.sha256
```
**On Windows (inside Powershell):** Run this command
From d8de405acc632d9ab91d5d681195b3abaf4913d7 Mon Sep 17 00:00:00 2001
From: Marc G <91296549+Marc-Gee@users.noreply.github.com>
Date: Thu, 2 Feb 2023 17:12:22 -0800
Subject: [PATCH 21/41] Inserted instructions on MicroSD writing.
1st draft of MicroSD.
Thus far I am holding back on elaborating on the DD usage, until the commands are tested some more.
I have/can insert screenshots of the Pi Imager/Etcher basic actions, but I am concerned its getting too long.
---
README.md | 27 ++++++++++++++++++++++++---
1 file changed, 24 insertions(+), 3 deletions(-)
diff --git a/README.md b/README.md
index de7e54a5..996f8328 100644
--- a/README.md
+++ b/README.md
@@ -213,9 +213,30 @@ Please recognize that this process can only validate the software to the extent
-## Writing the software to your MicroSD card
- Insert more instructions here.
- (to be done by MarcG)
+## Writing the software onto your MicroSD card
+
+To write the SeedSigner software onto your MicroSD card, there are a few options available:
+| Application | Description | Platform and official Source |
+|--------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------|
+| Balena Etcher | The application is called Etcher, and the company that wrote it is called Balena. Hence *Etcher by Balena* or *Balena Etcher* | [Available for Windows, Mac and Linux](https://www.balena.io/etcher#download-etcher) |
+| Raspberry Pi Imager | Produced by the Raspberry Pi organization. | [Available for Windows, Mac and Linux](https://www.raspberrypi.com/software/) |
+| DD Command Line Utility | Built-in to Linux and MacOS, the DD (Data Duplicator) is a tool for advanced users. If not used carefully it can accidentally format the incorrect disk! | Built-in to Linux and MacOS |
+
+Be sure to download the software from the genuine publisher.
+Either of the Etcher or Pi Imager software is recommended. Some seedsigner users have reported a better experience with one or the other. So, if the one application doesn’t work well for your particular machine, then please try the other one.
+
+### **General Considerations:**
+Make sure to set any write-protection physical slider on the MicroSD Card Adapter to UN-locked.
+You *dont* need to unzip the .zip file beforehand. You also don’t need to pre-format the MicroSD beforehand.
+Please use Etchers or Pi Imagers *verify* feature to make sure the card was written successfully! This can save a lot of effort troublsshooting issues where your seedsigner device doesn’t boot up or nothing displays on the SeedSigner screen at power on.
+Writing the MicroSd card is also known as flashing.
+It will overwrite everything on the MicroSD card.
+If the one application fails for you, then please try again using the other application.
+#### **Specific considerations for Windows users:**
+Windows can sometimes flag the writing of a MicroSD as risky behaviour and hence it may prevent this activity. If this happens, your writing/flashing will fail, hang or wont even begin, in which case you should to try to run the Etcher/Pi-Imager app "As administrator", (right-click and choose that option). It can also be blocked by windows security in some cases, so If you have the (non-default) *Controlled Folder Access* option set to active, try turning that *off* temporarily.
+
+
+Advanced users may want to try the Linux/MacOS *DD* command instead of Etcher or Pi Imager, however, a reminder is given that DD can overwrite the wrong disk if you are not careful !
---------------
From e901621ff91ae6494b4085142400b8dfbb9400a2 Mon Sep 17 00:00:00 2001
From: ValueOverflow <124897511+ValueOverflow@users.noreply.github.com>
Date: Mon, 13 Feb 2023 10:44:14 -0500
Subject: [PATCH 22/41] Add files via upload
The files may need to be in place before the readme.md can link to them. I'll submit a PR for an edited readme if these are approved for inclusion.
---
docs/21x21_A4_trading_card_2sided.pdf | Bin 0 -> 112100 bytes
docs/21x21_letter_trading_card_2sided.pdf | Bin 0 -> 101557 bytes
docs/25x25_A4_trading_card_2sided.pdf | Bin 0 -> 132136 bytes
docs/25x25_letter_trading_card_2sided.pdf | Bin 0 -> 130064 bytes
docs/29x29_A4_trading_card_2sided.pdf | Bin 0 -> 144916 bytes
docs/29x29_letter_trading_card_2sided.pdf | Bin 0 -> 143302 bytes
6 files changed, 0 insertions(+), 0 deletions(-)
create mode 100644 docs/21x21_A4_trading_card_2sided.pdf
create mode 100644 docs/21x21_letter_trading_card_2sided.pdf
create mode 100644 docs/25x25_A4_trading_card_2sided.pdf
create mode 100644 docs/25x25_letter_trading_card_2sided.pdf
create mode 100644 docs/29x29_A4_trading_card_2sided.pdf
create mode 100644 docs/29x29_letter_trading_card_2sided.pdf
diff --git a/docs/21x21_A4_trading_card_2sided.pdf b/docs/21x21_A4_trading_card_2sided.pdf
new file mode 100644
index 0000000000000000000000000000000000000000..01946eea088748a5fe06a930b8b5bac4d9214793
GIT binary patch
literal 112100
zcmdSBWmFv7)-K#QK@%icAh<*0?(Pr>5Zs*xf^pW$N&Ok{~z2+i1RWpJ&KPt{ynrEvQrCZ o8Pb5Q8R$;HK(p?+npK27m^bFC}Rcwq#&@KXHSj`bNm_q}Ww2d-^J$
zvFZp6B1sTwhDM>$lT*D;ti{^-+r@u|5fthyN{J)6PUfznzhhLEHnyv_vAefE_{`m3
ztA`PhQj(qmSyDtH$|uz~#R$N95Gd8MsM)ot?~{qMU1@#;i1XWIo57<9x7SF!u}>}E
zhR#Rze!-3}45%#K^&`1;wMx6(Vd|THrDIS^=bvJMw80=$BxG~EH|H*v!YI%JR@gcX
zR2ko&2$cvD;`2t?+7CLS#ti)aAIezcxpPtDCFv)obJT)?h#McL
z>^>j$uf0&hn-w
xAj_v+obyF6cKR|1;zOsemJ&O2JI
zlAfEpW#+Z3Y%A@PM~`NGn`2=(Rku%j+l1Wf#w?9x=lgI6C~N0E*U?QfX3xzGQ)k$T
zXc__h0>U^pmR!GoyoGkituL0HCn~ragn(ws_j?+ioA{acAZF5a`Igq31h&m{w;-G(
z00bCT?Ipxk?E3a;B>B-DIvm}+yt&SW(u?G@a(g9e^?rYq5wZ3lp@5ZJ#l(2^%2dgi
zYzG_(_b_aNr)!ko(a4`nLxAJUMKJmTv-sV$DsHgMa2Kdw6D1XHl}{{}ak`yhdCdud
z5@bs;-}Ie?8mtj%QJ>HwcQ3^w@hRR9Tk#%{sR@Yw>C?4)Pbp`pD|-u$F#;uw#DX0a
zlfNDa>7
mr-b$1*qHtad1scSFC{5yQtcNpvI?V8s1Q4Q!iWHL-)()Y
zAQc|F#W)`xwLD$C4zPjK+0nzv){$lKZDLV>JlNaX40SRo_zgM0iHj(xt(8H;13~BI
zlcP}Eo
